NIST SP 800-171 Documentation: SSP, POA&M and Policies
A system security plan (SSP) describes how each NIST SP 800-171 requirement is implemented in your environment. SENTRE’s SSP, policies and procedures start from documentation that has passed a C3PAO assessment, then are adapted to you.
What documentation does NIST SP 800-171 require?
NIST SP 800-171 expects you to document how your systems protect Controlled Unclassified Information (CUI) and to keep that documentation current. The System Security Plan is the anchor: requirement 3.12.4 calls for one, and every assessor starts there, whether the assessment is your own, DCMA’s or a C3PAO’s.
Around the SSP sit plans of action for open items, policies and procedures for each requirement family, and the records that prove the requirements operate: logs, changes, incidents, training and scans. Contractors that handle CUI for the Department of War (DoW, also DoD) also need an incident response plan that covers the DFARS 7012 report.
The same set supports a self-assessment, a DCMA assessment or a voluntary C3PAO assessment CMMC Level 2 →. What changes between them is who reads it, not what it has to say. A plan that holds up in one holds up in the others.
What documentation comes with SENTRE?
| Deliverable | Purpose | Who maintains it |
|---|---|---|
| System Security Plan (SSP) | Boundary, components, users and how each of the 110 requirements is implemented | ITG, as part of the managed service |
| Incident Response Plan | How incidents are detected, handled, recorded and reported, incl. the 72-hour DFARS 7012 report | Kept current with the SSP |
| Policies and Procedures | Rules and steps for each requirement family, fitted to your roles and approval chains | Your team, with ITG |
| Work Instructions | Step-by-step CUI handling across awards, orders, supply chain, invoicing and delivery | Your team, trained by ITG |
| Configuration Management Plan | Baselines for the enclave and how changes are proposed, approved, tested and recorded in CENTRE | ITG, through change management in CENTRE |
| Plan of Action and Milestones (POA&M) structure | Open items, owners and dates, tracked with the SSP | Your team |
| Shared Responsibility Matrix | Who is responsible for each requirement: ITG, your team, or both | Reference for your SSP |
How is your documentation built?
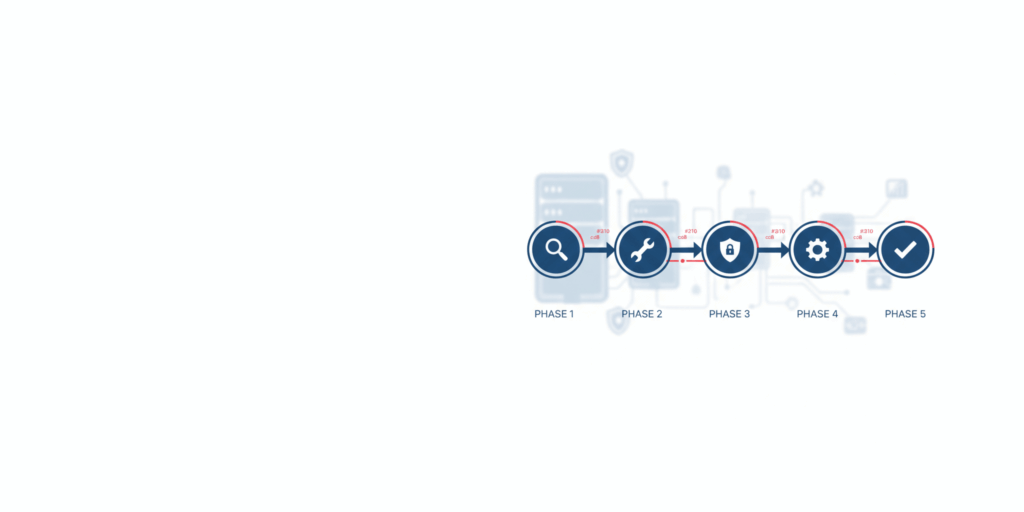
1
Start From Assessed Docs
Begin with the documentation ITG used in its own C3PAO assessment, not a blank template.
2
Map Your Boundary
Describe your enclave, its components, its users and the CUI flows found in Discovery.
3
Adapt Roles and Steps
Fit policies, procedures and work instructions to your roles, approval chains and contracts.
4
Validate on the Enclave
Check every statement in the SSP against the enclave as configured, before go-live.
5
Hand Over
Your team takes over policies, procedures and work instructions. ITG keeps the SSP and configuration records current in CENTRE.
What makes a system security plan hold up in an assessment?
An SSP holds up when it matches the system you actually run, covers every requirement and is visibly current. Assessors compare the plan with the live environment, interview the people who operate it and test the requirements; a plan describing a system you do not run becomes a finding.
Each of the 110 requirements needs an implementation statement, including those the Shared Responsibility Matrix assigns to your organization. Dates, versions and owners show the plan is maintained, not written once for an assessment and left alone.
Documentation drifts when it lives apart from operations. In SENTRE, the SSP and records sit in CENTRE’s document control, linked to their requirements, and change records update them as the enclave changes. Evidence is produced by daily operations, not assembled before an assessment, and an annual review lines the documents up ahead of each affirmation.
Templates are a starting point, not an SSP
An SSP template can show the structure, but only your environment can fill it in. SENTRE documentation starts from a real, assessed environment: ITG spent more than 10 months building and documenting it before a C3PAO assessed it at 110 of 110. ITG adapts it to your organization during implementation. After go-live ITG keeps the SSP and configuration records current, and your team keeps policies, procedures and work instructions in step with how your people work.
How does documentation stay current?
In SENTRE, documentation lives with operations. The SSP and records sit in CENTRE’s document control, linked to their requirements, and change records update them as the enclave changes.
- Version-controlled SSP, policies and procedures
- Changes approved and traced in CENTRE
- Evidence produced by operations, not assembled before an assessment
- An annual review ahead of each affirmation
- Training records linked to the people who handle CUI
Who keeps the documentation current?
The documentation is yours, and ITG keeps it current. ITG adapts the SSP, policies, procedures and work instructions to your enclave during implementation and validates them against the system as built. After go-live they sit in CENTRE’s document control, and ITG updates the SSP as part of the managed service as people, contracts and configurations change.
The Shared Responsibility Matrix lists which requirements ITG, your team or both are responsible for, and the SSP’s implementation statements follow it. When a change touches the enclave, ITG records it through change management and updates the configuration records with it.
The incident response plan is delivered the same way: written from an assessed environment, adapted to your organization, validated during implementation and kept current with the SSP, including the DFARS 7012 reporting step to DoW.
CMMC documentation FAQs
What is a system security plan?
An SSP describes your system boundary, environment and how each NIST SP 800-171 requirement is implemented. Requirement 3.12.4 calls for it, and it is the first document an assessor reads. Without one, there is nothing to assess and no score to post.
When is a POA&M allowed?
A plan of action and milestones lists requirements not yet met, with owners and dates. Under CMMC Level 2, only some requirements may be on a POA&M, and items must be closed within 180 days. Check the current rule text before relying on one.
Can we use an SSP template?
As a structure, yes. As your SSP, no: it must describe your actual system, your boundary and the way your people work. A template without a matching environment is a common assessment finding, because the plan and the system tell different stories.
Who maintains the documentation?
ITG keeps the SSP and configuration records current as part of the managed service, using CENTRE’s document control and change records. Your team keeps policies, procedures and work instructions in step with how your people work, and ITG helps when a change affects the plan.
How does it support our affirmation?
The affirmation states that the requirements are still met. A current SSP and records from daily operations are what that statement rests on, and they are what DCMA or an assessor will ask to see if the statement is ever tested. SPRS score →
Is it the same documentation as ITG’s?
It starts from the documentation ITG used in its own C3PAO assessment, with enterprise scope, and is adapted to your organization, roles, contracts and processes during implementation. What you receive describes your enclave, your people and your boundary, not ITG’s.
See which documentation SENTRE would give your organization, and how it fits your processes. Discovery is a no-obligation review.